Resilient Security for Financial Institutions
Proactive, resilient defense is essential for protecting assets, ensuring compliance, and maintaining market confidence in an AI-driven world.
Talk to an ExpertHigh-Stakes Cyber Risks
In 2026, financial institutions face an unrelenting storm. A single breach can result in massive financial losses, regulatory fines, and eroded customer trust.
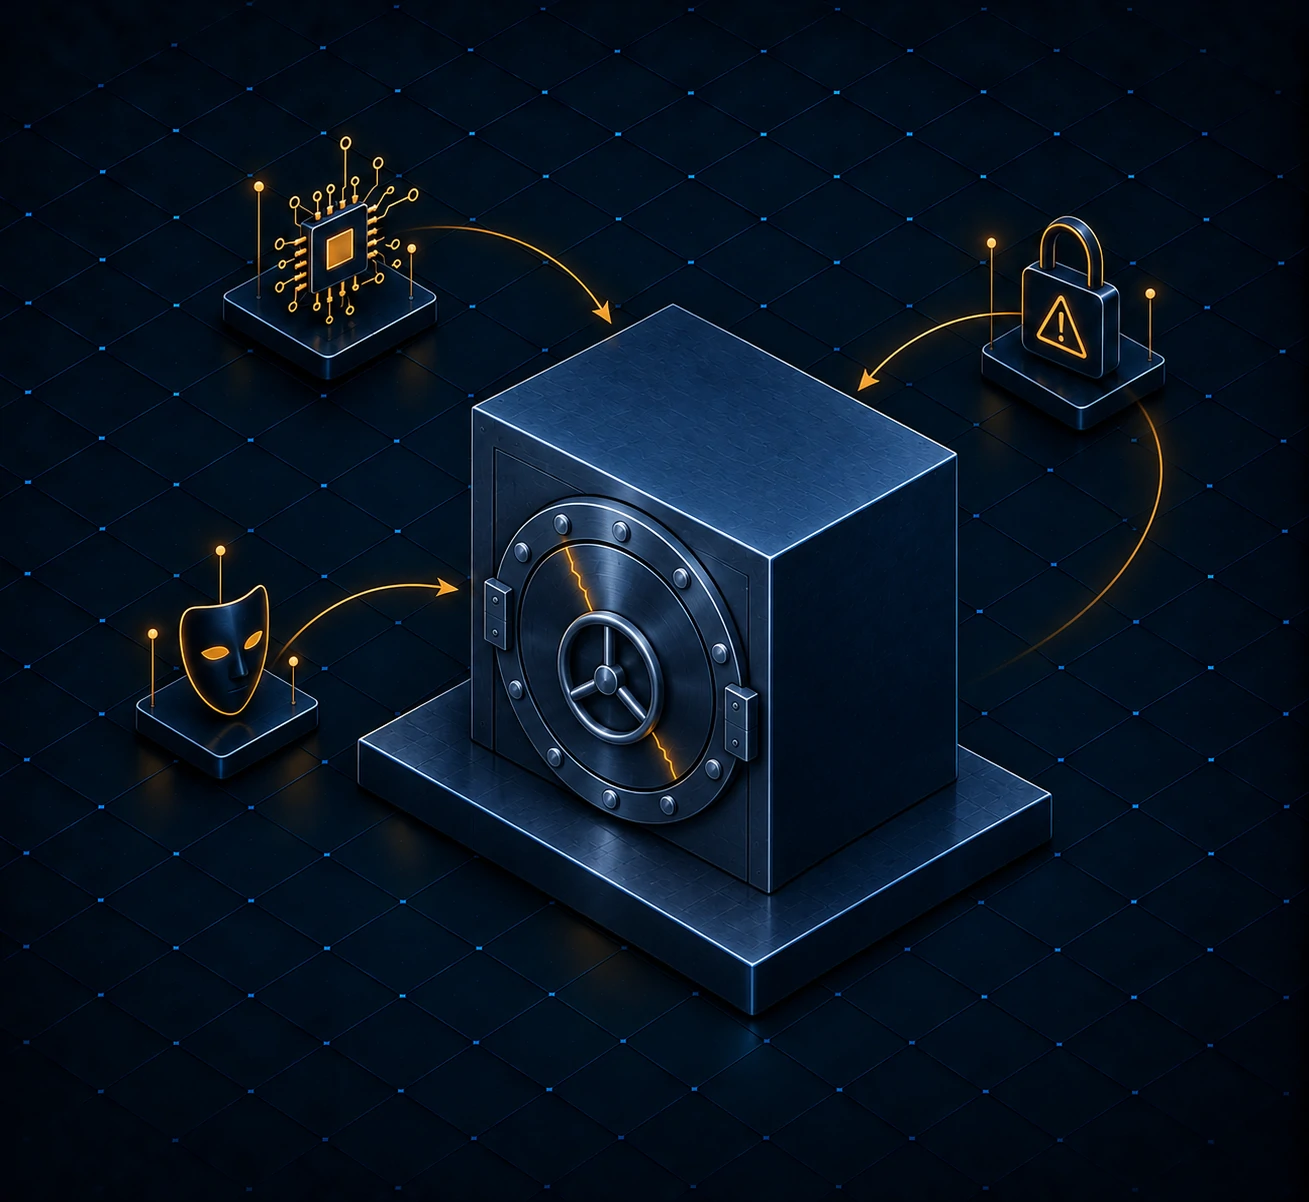
AI-Driven Threats
Automated attacks powered by AI that adapt faster than traditional defenses.
Ransomware Surges
A 9% year-on-year increase in targeted attacks aiming to cripple operations.
Deepfake Fraud
Synthetic identities and deepfake voice/video enabling sophisticated fraud.
Supply Chain Risk
Vulnerabilities in third-party software impacting critical banking infrastructure.
Regulatory Pressure
Tightening mandates like DORA, NIST, and CMMC requiring strict compliance reporting.
Reputational Damage
Loss of customer trust and market value following high-profile data breaches.
How Delve Risk Helps You Navigate These Challenges
Delve Risk delivers cybersecurity-first managed services tailored to financial services.
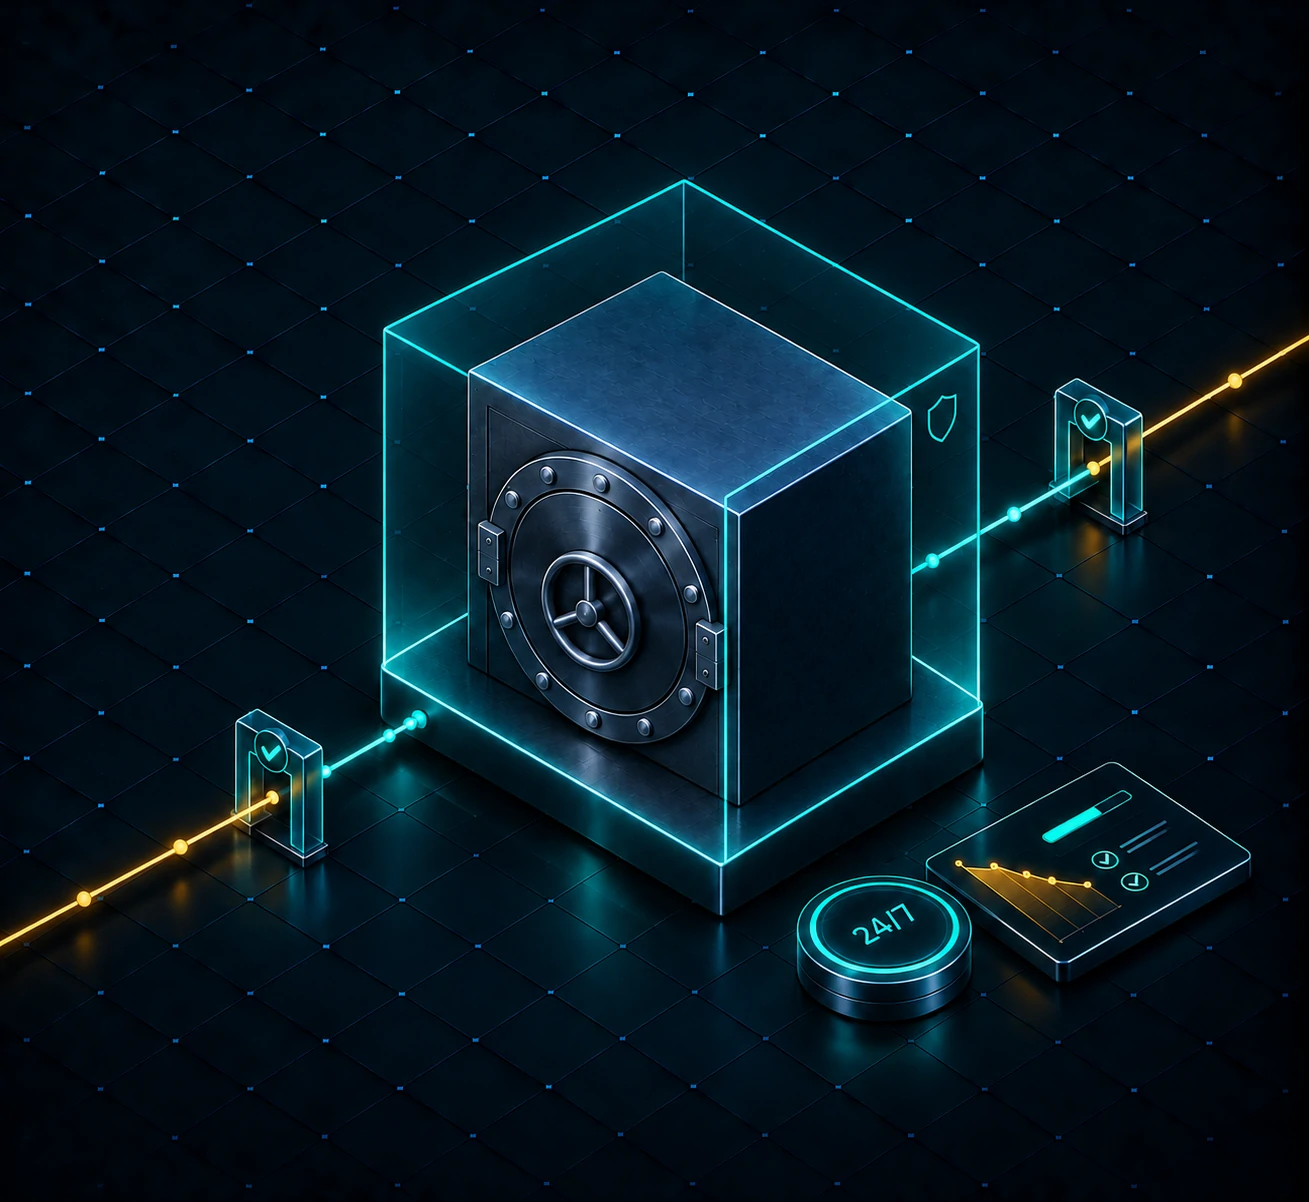
Secure Architectures
We build secure, Zero Trust architectures and Cloud First infrastructures on Microsoft Azure/M365 with embedded compliance controls.
Seamless Migration
Migrate legacy systems seamlessly while hardening against emerging AI threats.
Proactive Defense
Maintain 24/7 proactive monitoring, automated vulnerability management, and rapid incident response.
Full Accountability
We take full accountability for your security posture—providing executive dashboards, measurable risk reduction, and audit-ready compliance (PCI-DSS, SOX, FINRA, etc.) so you focus on growth.
Common Questions
What cyber risks do financial institutions face?
AI-driven threats, ransomware, deepfake fraud, supply chain risk, regulatory pressure from mandates such as DORA, NIST, and CMMC, and reputational damage after high-profile breaches.
How does Delve Risk help financial institutions?
By building secure Zero Trust architectures and Cloud First infrastructures on Microsoft Azure and M365 with embedded compliance controls, migrating legacy systems while hardening against emerging AI threats, and maintaining 24/7 proactive monitoring, automated vulnerability management, and rapid incident response.
Which compliance requirements does Delve Risk support?
Audit-ready compliance including PCI-DSS, SOX, and FINRA, along with executive dashboards and measurable risk reduction.