Compliance and Regulatory Assessments
Turning Compliance into Confidence. Delve Risk transforms complex regulatory requirements into strategic advantages.
Talk to an ExpertStreamline Compliance with a CRI-Aligned Cybersecurity Assessment
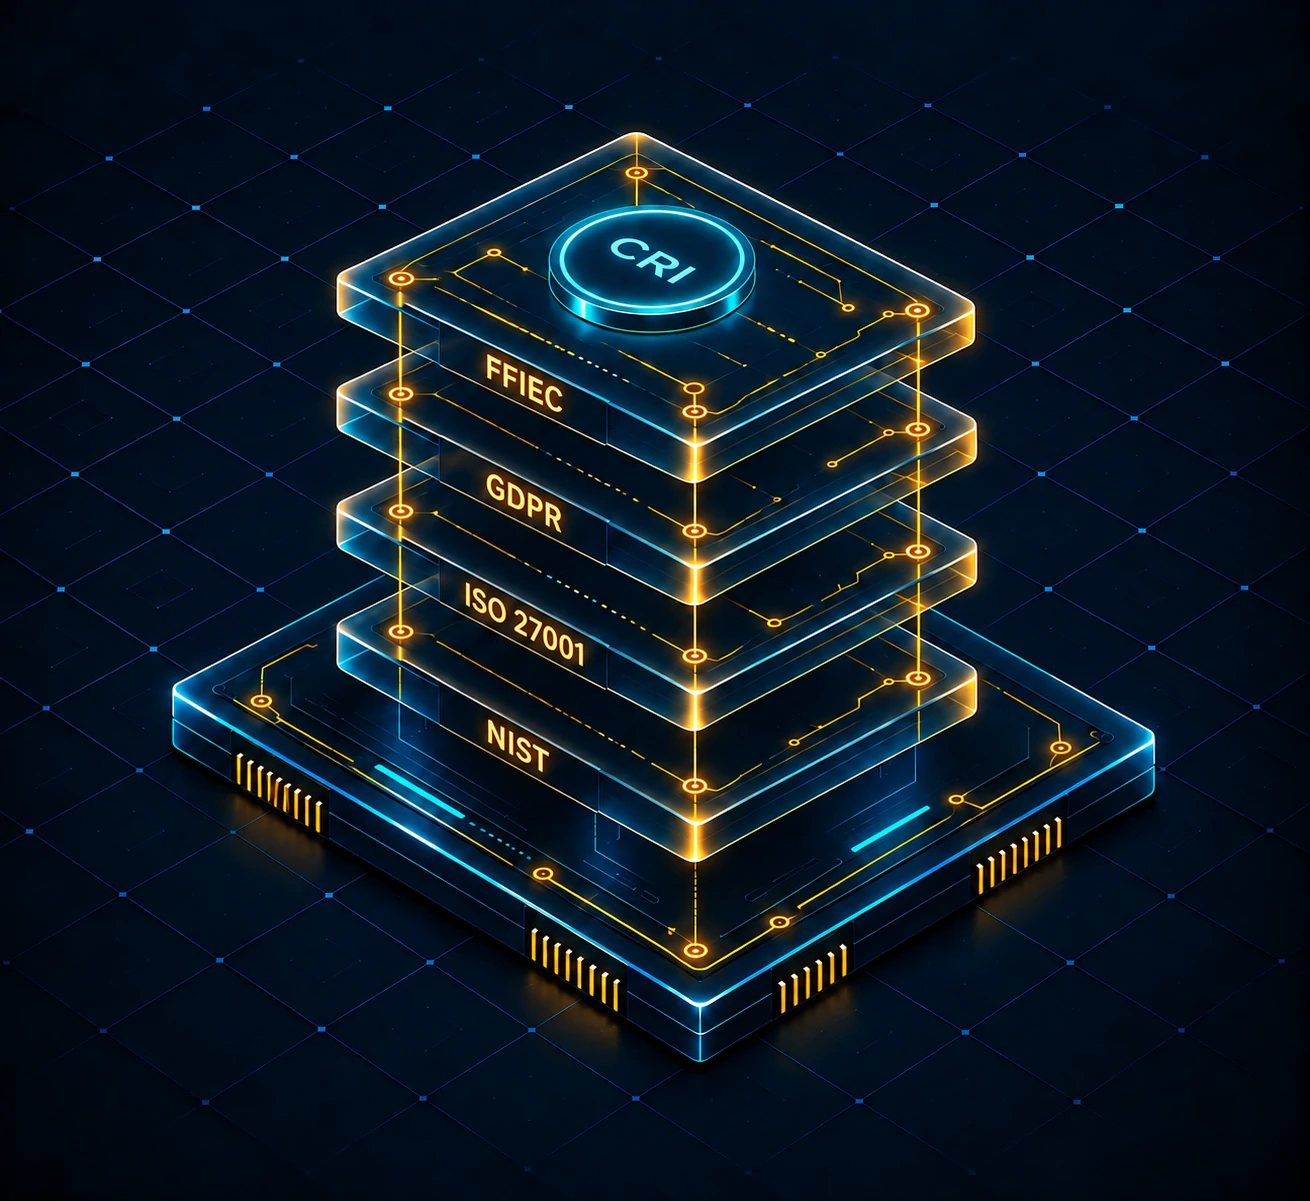
The CRI Cybersecurity Profile Assessment is a risk-based framework designed specifically for the financial sector. Built on the NIST Cybersecurity Framework and extended to align with global regulatory expectations (including ISO 27001, GDPR, and FFIEC), the Profile streamlines compliance and cybersecurity operations. Delve Risk is one of the few firms offering CRI-aligned assessments, giving your organization a scalable way to meet increasing demands from regulators and internal stakeholders.
Internal Stakeholders
Scalable way to meet increasing demands.
Global Standards
Extended to align with global regulatory expectations.
Risk-Based Framework
Designed specifically for the financial sector.
CRI Aligned
ISO 27001 verified. SOC 2 Type II active.
Empowering your organization with streamlined compliance programs and actionable insights.
Security Consulting
Tailored guidance to align your security program with business goals and industry best practices.
Staff Augmentation
Enhance your team with on-demand security professionals to meet urgent or long-term needs.
Strategic Program Development
Collaborate on roadmap creation, policy design, and governance frameworks for a more mature security posture.
Virtual CISO (vCISO)
Executive-level security leadership without the full-time cost—ideal for scaling teams or filling a critical gap.
Our comprehensive assessment platform covers a vast array of regulatory standards.
Ensuring your organization remains compliant regardless of industry or region.
Global Reach
Standards applicable across North America, Europe, and APAC.
Industry Specific
Tailored frameworks for Finance, Healthcare, Gov, and more.
Continuous Updates
Always up-to-date with the latest regulatory changes.
Turning Compliance into Confidence
The Challenge
- Limited expertise
- Resource strain
- Audit & risk exposure
The Solution
- Specialized expertise
- Efficient, scalable solutions
- Proactive risk reduction
“Delve Risk delivers tailored, practical solutions with clear next steps, so you can close gaps quickly and confidently without getting lost in compliance jargon.”
Common Questions
What is a CRI-aligned cybersecurity assessment?
The CRI Cybersecurity Profile Assessment is a risk-based framework designed specifically for the financial sector. It is built on the NIST Cybersecurity Framework and extended to align with global regulatory expectations, including ISO 27001, GDPR, and FFIEC.
Which compliance frameworks does Delve Risk cover?
More than 70 global frameworks, including CMMC, ISO 27001, COBIT, NIST CSF, PCI, FedRAMP, HIPAA, GDPR, CRI, SOC 1 and 2, and CIS, with standards applicable across North America, Europe, and APAC.
What services support a compliance program?
Security consulting, staff augmentation, strategic program development (roadmaps, policy design, and governance frameworks), and virtual CISO (vCISO) leadership.
What is a vCISO?
A virtual CISO provides executive-level security leadership without the full-time cost, which suits scaling teams or organizations filling a critical gap.