01
Vulnerability Assessment
A comprehensive inventory of your company’s assets and their security posture, including network devices, web applications, and databases.
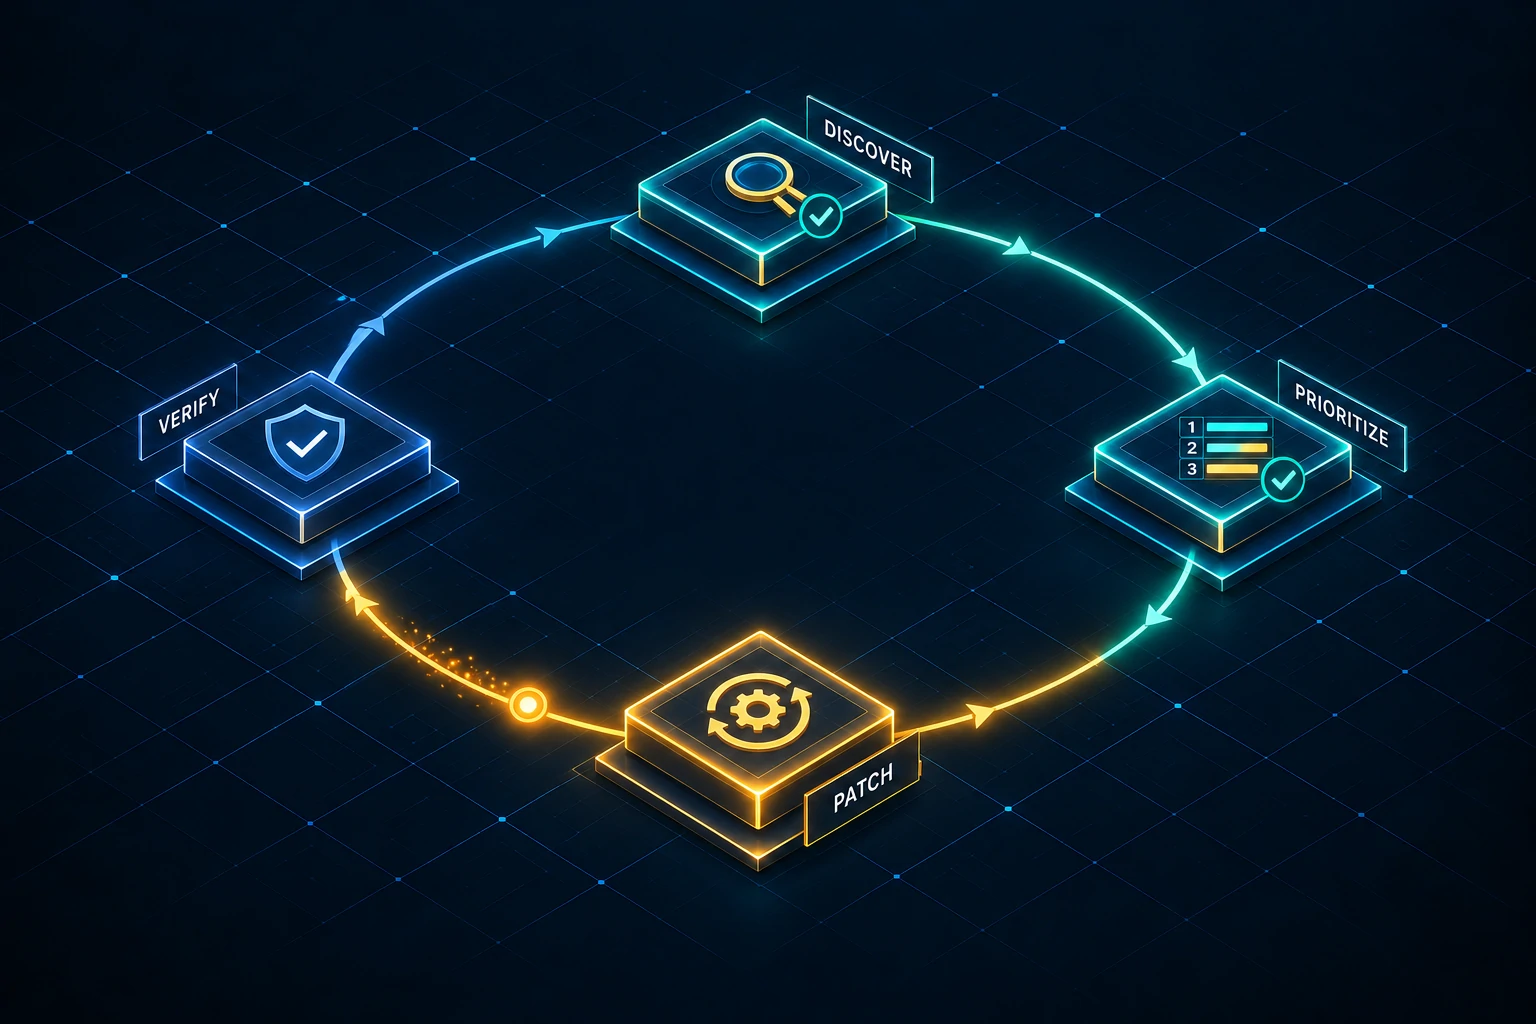
Delve Risk delivers proactive, risk-based vulnerability management and consistent patch deployment, ensuring your critical assets remain secure, resilient, and protected against emerging threats.
Talk to an ExpertVulnerabilities are weaknesses in software that hackers can exploit to access networks, steal sensitive data, and compromise assets.
Given the complexity and scale of tracking every system manually, companies increasingly rely on automated vulnerability management solutions like ours.
A comprehensive inventory of your company’s assets and their security posture, including network devices, web applications, and databases.
Automatically manages the deployment of patches to ensure systems remain up-to-date with the latest software versions and vendor-fixed vulnerabilities.
Detailed reports highlight findings from assessments and document actions taken during patch management, such as deployments and updates.
Rapid detection and prioritization of critical vulnerabilities using industry-leading scanning and threat intelligence tools to minimize the window of exploitation.
Vulnerabilities are ranked by real-world business risk, ensuring your team focuses on what matters most.
Clear dashboards and reporting provide 24/7 insight into your security posture and remediation progress.
Automates scanning, tracking, and patching to eliminate manual work and speed up security operations.
“Delve Risk takes a proactive, strategic approach to vulnerability management—uncovering threats early, prioritizing what matters most, and ensuring consistent remediation so you can stay focused on running your business while we handle the protection.”
Vulnerabilities are weaknesses in software that hackers can exploit to access networks, steal sensitive data, and compromise assets. Vulnerability and patch management finds those weaknesses, ranks them, and deploys the vendor-fixed patches that close them.
A comprehensive inventory of your company's assets and their security posture, including network devices, web applications, and databases.
Vulnerabilities are ranked by real-world business risk, so your team focuses on what matters most. Industry-leading scanning and threat intelligence tools support rapid detection and prioritization of critical vulnerabilities, minimizing the window of exploitation.
Yes. Patch management automatically manages the deployment of patches so systems stay up to date with the latest software versions and vendor-fixed vulnerabilities. Scanning, tracking, and patching are automated, and detailed reports document the actions taken.